On October 15, 2026, GitHub announced general availability of agentic autofix for code scanning alerts. For businesses with a custom online shop, booking system or internal application, it offers another way to ask AI to prepare fixes for potential vulnerabilities already detected. The developer retains the final decision.
What changed
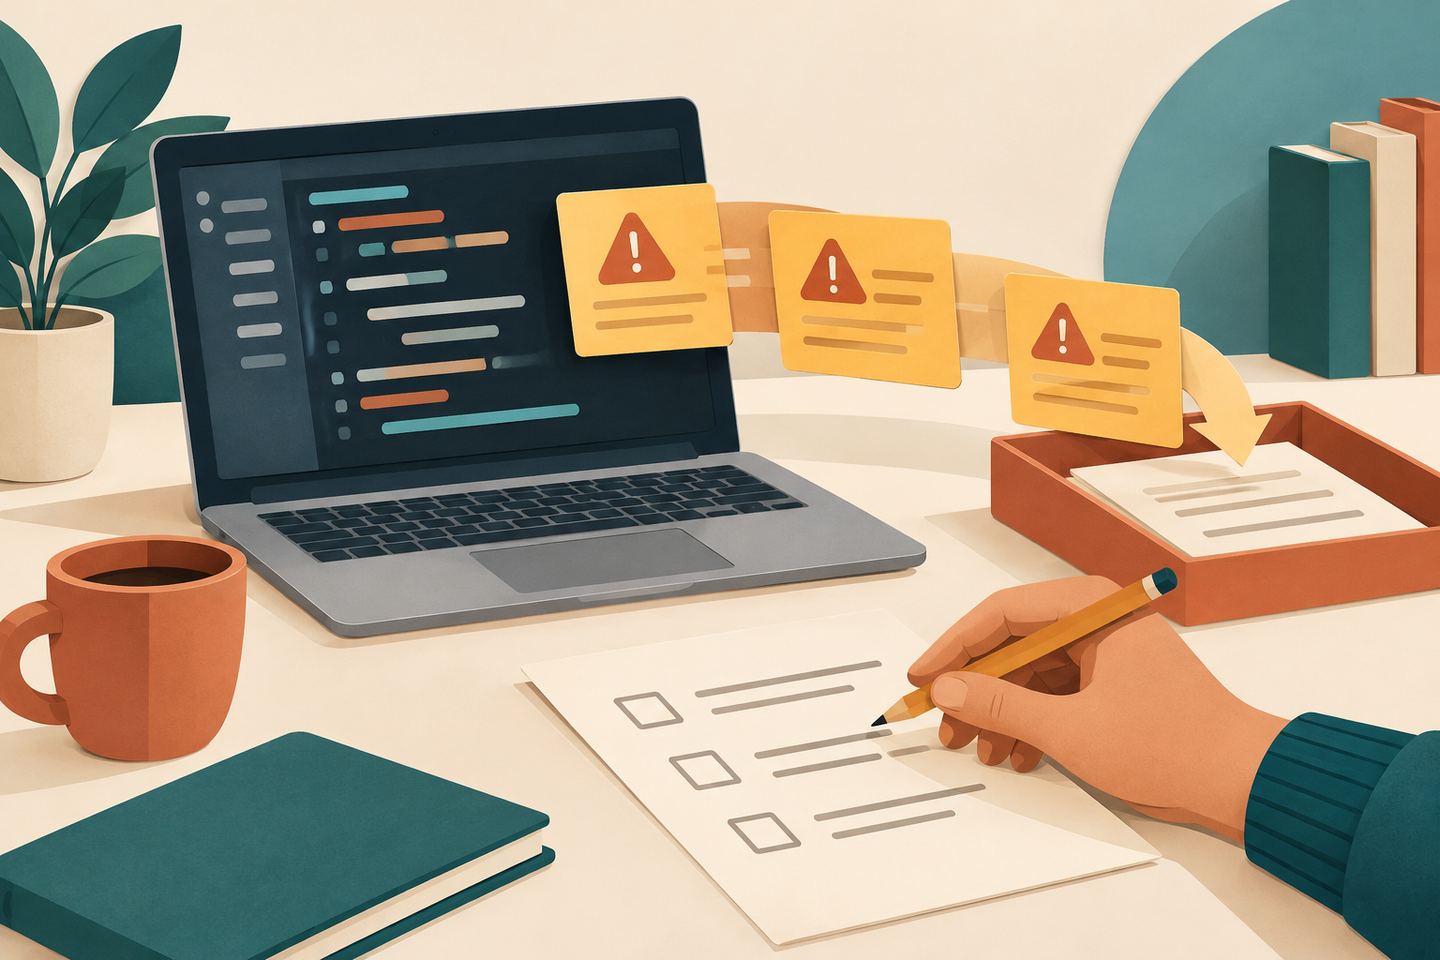
According to GitHub’s announcement, the agent investigates related files, proposes changes, reruns CodeQL and opens a draft pull request, a proposal to change code. It works on the alert backlog in the repository’s default branch. The documentation allows one assignment to group up to 25 alerts into one session and one pull request.
Availability and costs
Current documentation specifies access for public GitHub.com repositories and organization-owned repositories with GitHub Code Security or GitHub Advanced Security. A Copilot license is not required. Repositories in Enterprise Managed Users’ personal namespaces are unsupported.
The feature must be enabled; organizations that used the public preview must enable it again. Organization-level enablement covers eligible repositories by default, so administrators should identify exceptions beforehand.
Sessions consume Code Security AI Credits and GitHub Actions minutes, including in public repositories. Included credits are used first if the billed account has them; usage is metered after they run out, or from the start if none are included. Check billing configuration and the budget for these costs before running it.
Limits of automated validation
GitHub describes validation as best effort, without a guarantee of success. The agent cannot confirm fixes for custom CodeQL queries, the security-extended suite or third-party tool alerts. Generated changes should be reviewed and tested before merging. Classic Copilot Autofix is a separate suggested-fix workflow that does not consume AI Credits.
What to ask your developer
Our editorial recommendation is to start with a small group of alerts in one repository. Agree a spending ceiling, a code reviewer and checks of normal workflows after the change, such as checkout. This is a proposed testing approach, not a measured deployment result.
Bottom line: agentic autofix can prepare a draft technical fix; it does not establish the security of an entire website. Nadali has not tested the feature or time savings.
Author: Nadali. Prepared using AI. Sources checked on October 19, 2026.