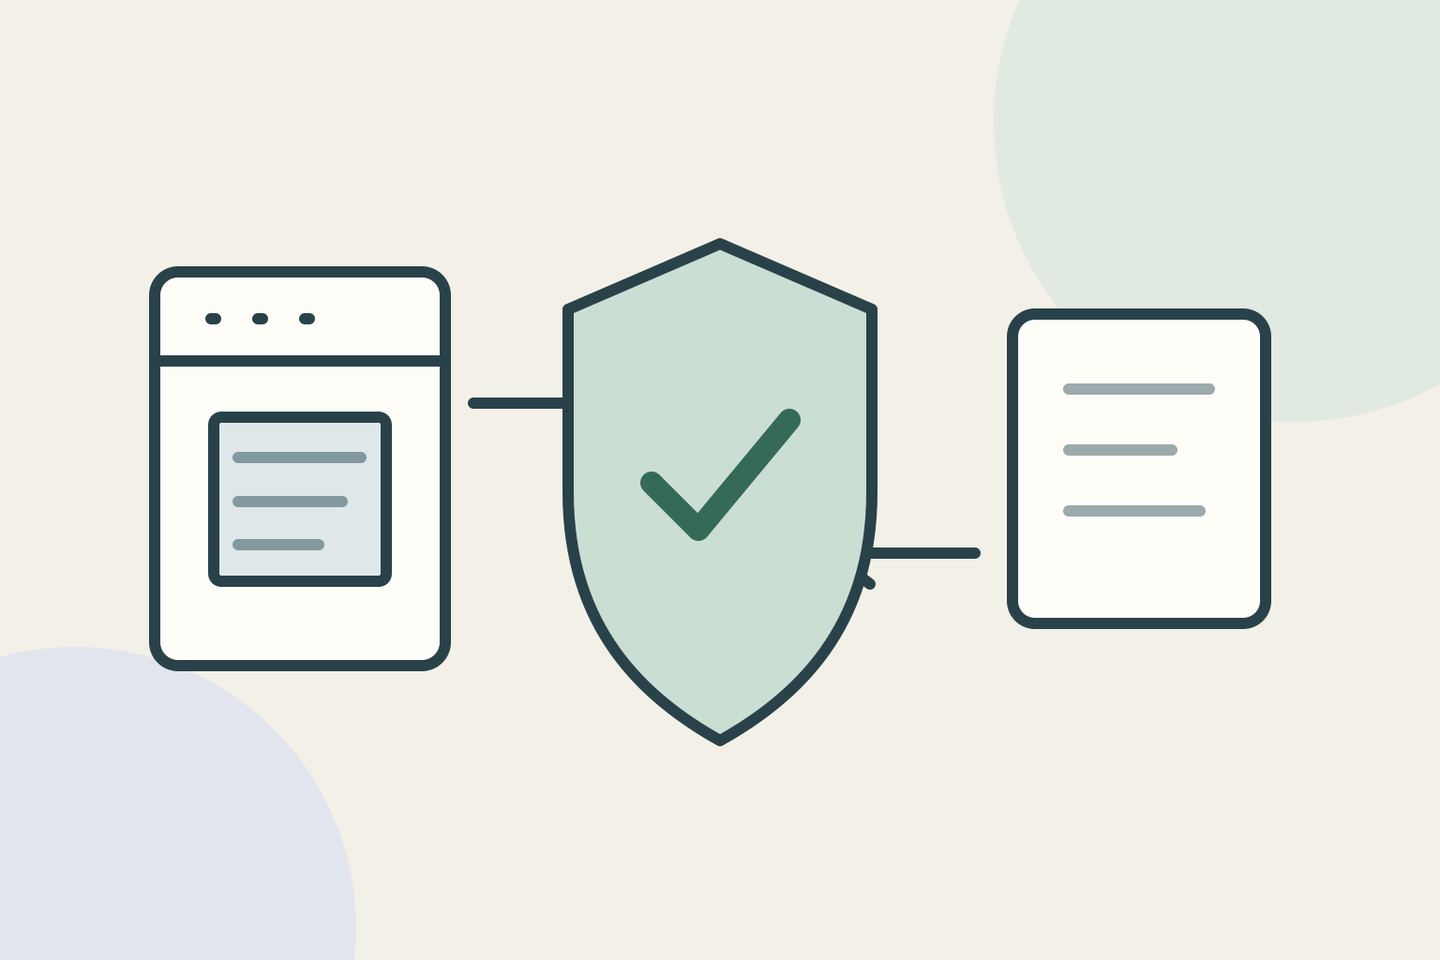
On October 21, 2026, Cloudflare launched combined request-response checks for proxied websites, including Free plans.
Who benefits
Owners of shops, hotels and other businesses with their own websites. The practical question for a contractor: is protection configured for the server’s outgoing response as well as the incoming request?
In its PHP vulnerability protection announcement, Cloudflare specifies that its Managed Response Firewall Default ruleset was automatically deployed across plans. It also urges customers to check active rules and apply PHP fixes. Nadali has not inspected your website configuration.
What to ask the person responsible
Nadali’s suggested sequence:
- Ask which website domains actually pass through Cloudflare and who owns their protection. Do not infer this from the hosting provider’s name alone.
- Ask to see active rules under Security → Security Rules and have their scope explained. Record the inspection date and responsible person.
- Arrange checks of ordinary enquiries, bookings or orders using non-sensitive test data. If legitimate activity is blocked, give the administrator the time and scenario rather than disabling protection at random.
- Separately obtain confirmation of installed server updates. Having a filter does not complete that task.
This is a proposed workflow, not a result of our testing.
Availability and limits
Blocking a response cannot undo actions the server has already performed. The business takeaway: verify the additional protection while keeping updates and website workflow checks as separate required tasks.
Read also about checking PHP fixes with your hosting provider.
Author: Nadali. Prepared with AI. Sources checked on October 23, 2026.